David Finn, executive vice president of strategic innovation at CynergisTek, a cybersecurity consulting firm, suggests that healthcare providers should take a reasoned, common sense approach to developing a cybersecurity program, according to an article on the Search Health IT website.
Finn suggested providers scale their security programs and understand they're not going to fix everything at once.
Healthcare providers should prioritize risks, determine what is most important to the organization and then start building it.
Every organization should have a designated security person, but the technology risks come down each staffer. People leave their machines logged on or click on email that they shouldn't, Finn said.
 Elevating EVS Professionals: The Case for Certified Hygiene Specialists
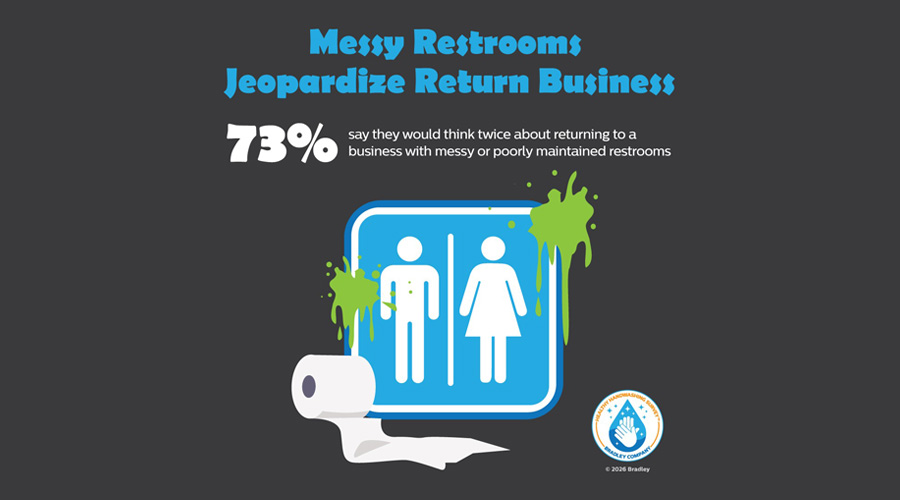 Global Handwashing Day and the Importance of Well-Maintained Restrooms
 Duke Health and CaroMont Health Partner to Develop Two New Hospitals
 Designing for the Psychology of Waiting
 UT Health Sciences Breaks Ground on College of Medicine Interdisciplinary Building