The recent ransomware attack on MedStar Health’s computer systems came through from a well-known security vulnerability in an application server, according to an article on the Healthcare Finance website.
The attack occurred after hackers discovered that MedStar uses JBoss, an application server with a recognized design flaw. The hackers used a virus-like software to scan the Internet for vulnerable JBoss servers.
Security researchers found that the JBoss application server was routinely misconfigured to allow unauthorized outside users to gain control.
The US government, Red Hat Inc., and other groups released warnings about the security issue in February 2007 and March 2010. MedStar could have fixed the vulnerability by installing a patch for the system or manually deleting two lines of software code.
 Extreme Weather: The Maintenance-Resilience Link
 Encompass Health Lower Providence Opens in Pennsylvania
 Intermountain Health Acquires Fairbourne Building for Healthcare Hub and Medical Campus Conversion
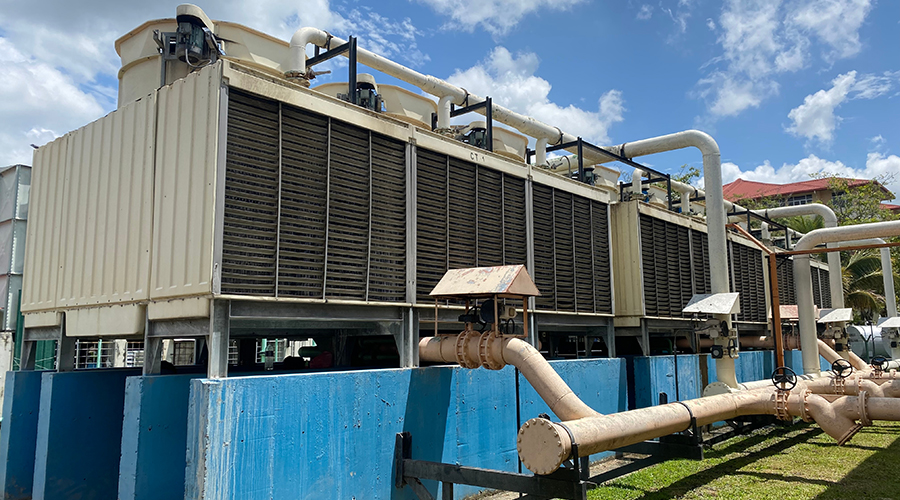 Cooling Towers at NYC Health + Hospitals/Lincoln Test Positive for Legionella
 Prefabricated Wall Panels Accelerate UCF Lake Nona Medical Center Construction