A new SecurityScorecard report says healthcare workers lack basic security awareness and points to a heightened risk of attacks through social engineering, according to an article on the Healthcare Informatics website.
The report calls employees "low-hanging fruit" for social engineering attacks.
“While a hospital’s IT department may be up to date and proficient at security standards such as DNS health and endpoint security, employees such as medical personnel, administrative professionals, among others, within a healthcare organization may not necessarily prioritize information security."
The low Social Engineering scores among a multitude of healthcare organizations show that security awareness and employee training are likely not sufficient and this poses a real risk to those organizations, the report said.
 Elevating EVS Professionals: The Case for Certified Hygiene Specialists
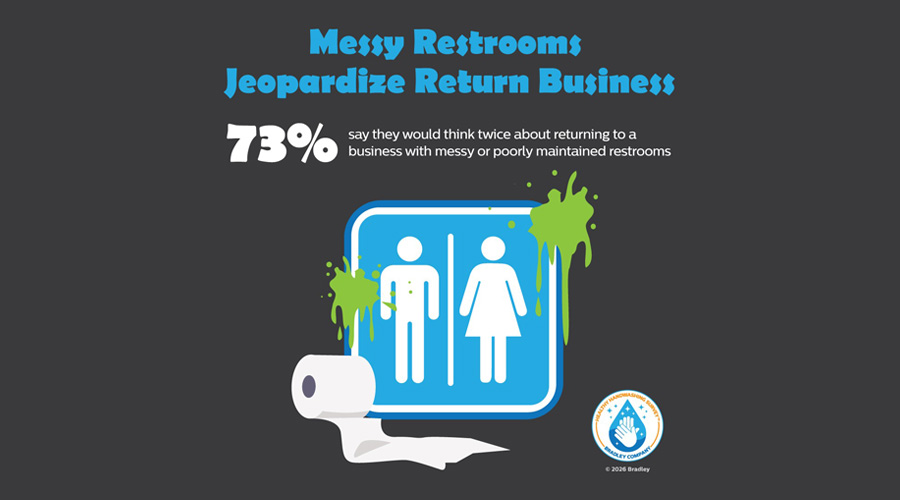 Global Handwashing Day and the Importance of Well-Maintained Restrooms
 Duke Health and CaroMont Health Partner to Develop Two New Hospitals
 Designing for the Psychology of Waiting
 UT Health Sciences Breaks Ground on College of Medicine Interdisciplinary Building